Enterprise networks were designed for a world in which most users worked in offices, most applications lived in corporate data centers, and internet access could be secured through a central perimeter. That model no longer reflects how many organizations operate.
Employees connect from anywhere. Business applications run across SaaS platforms, public clouds, and private environments. Partners and contractors need controlled access to specific services. Meanwhile, security teams must maintain visibility and enforce consistent policies without creating unnecessary friction.
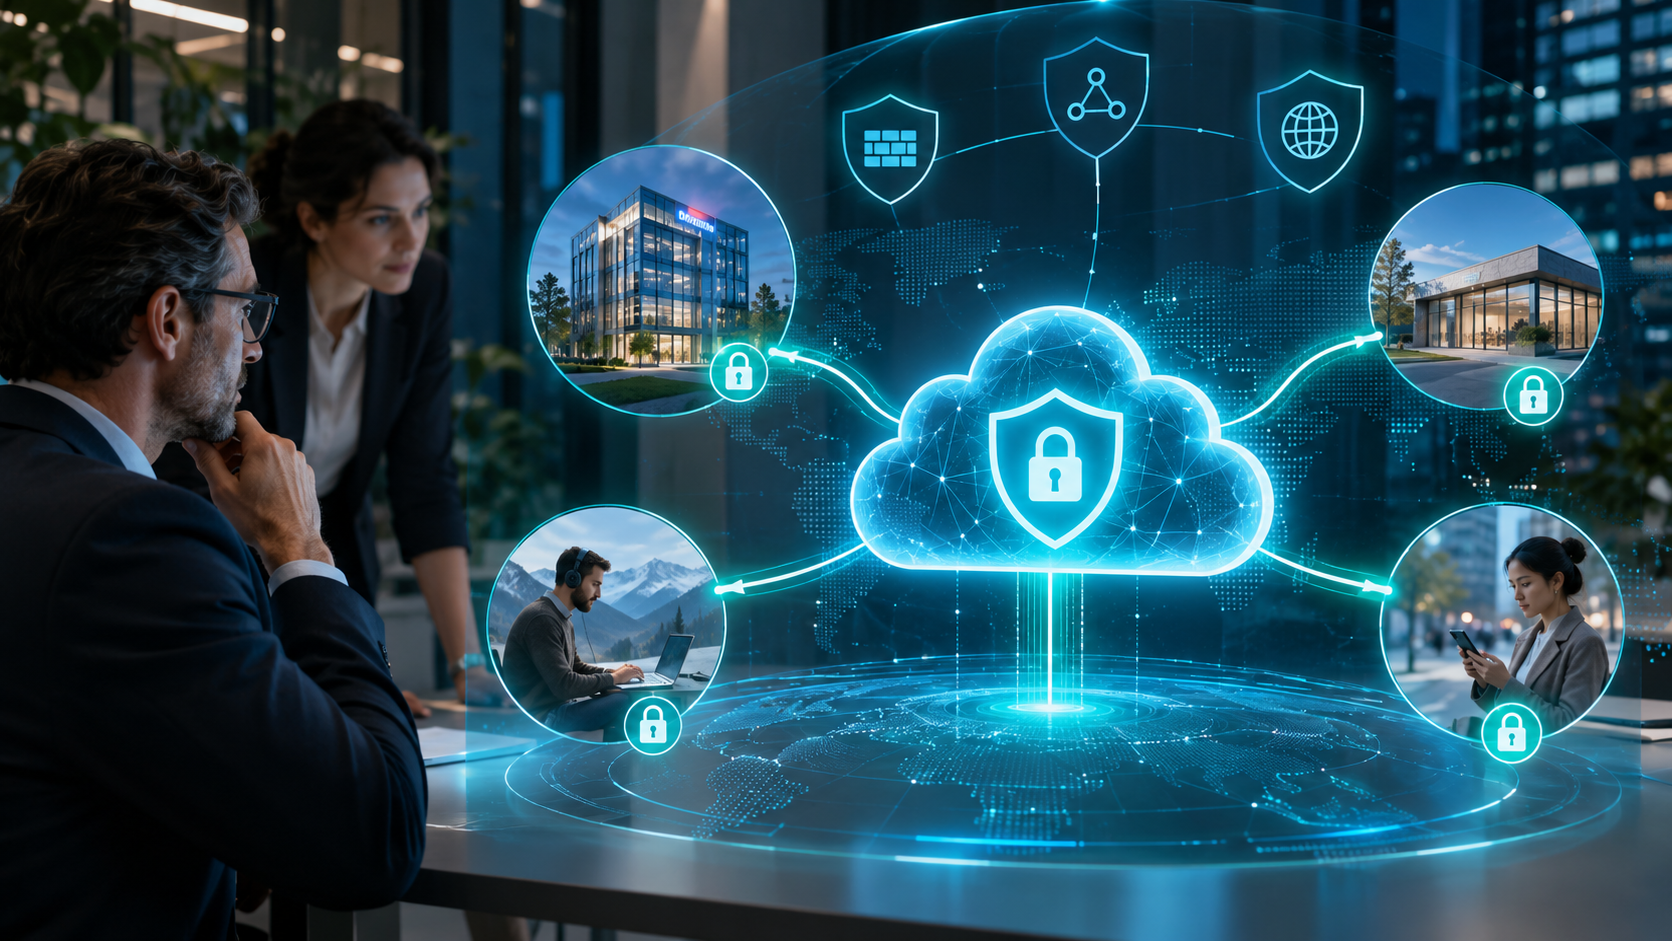
Secure Access Service Edge (SASE) is an architectural response to this change. It brings networking and cloud-delivered security capabilities together to support secure, efficient access to applications and data wherever users and resources are located.
However, purchasing a SASE platform does not automatically deliver Zero Trust or simplify operations. The value comes from the architecture, the policies, the migration plan, and the extent to which the organization adopts the new operating model.
What is SASE?
SASE stands for Secure Access Service Edge. It describes an approach that converges wide-area networking and cloud-delivered security services into a more integrated architecture.
Rather than sending every connection through a central data center for inspection, a SASE design can route users and branch traffic to appropriate distributed enforcement points. Security decisions can then consider identity, device posture, application, destination, and other relevant context.
SASE is not a single protocol, an appliance, or a guarantee that every function comes from one vendor. It is an architectural model; the practical quality of integration, inspection, traffic steering, observability, and policy management varies between implementations.
The essential components of SASE architecture
Most descriptions of SASE include networking and security capabilities that work together. Understanding their distinct roles helps organizations avoid treating the architecture as a checklist of product licenses.
SD-WAN: connecting locations and optimizing traffic paths
Software-Defined Wide Area Networking (SD-WAN) helps organizations manage and steer traffic across available connectivity options. It supports branch connectivity, path selection, and application-aware traffic policies. In a SASE strategy, the networking component determines how traffic reaches applications and security services.
SWG: protecting internet access
A Secure Web Gateway (SWG) inspects web activity and helps enforce policies against malicious destinations, inappropriate content, and risky downloads. Its role remains important even when employees access the internet directly from remote locations.
CASB: governing cloud application use
A Cloud Access Security Broker (CASB) provides visibility and policy control over cloud applications. Depending on its deployment mode and capabilities, it can support sanctioned application governance, shadow IT discovery, and protection of sensitive information in SaaS environments.
FWaaS: extending firewall controls through the cloud
Firewall as a Service (FWaaS) delivers relevant network security inspection and policy enforcement through cloud infrastructure. The goal is to apply consistent controls without depending exclusively on physical firewall appliances at individual sites.
ZTNA: restricting access to specific applications
Zero Trust Network Access (ZTNA) is designed to grant access to authorized applications based on identity and contextual policy, rather than exposing broad network connectivity by default. It can reduce unnecessary reachability and help replace selected remote-access VPN use cases, although migration requires careful application and dependency analysis.
Data protection, visibility, and policy integration
Many implementations also incorporate data loss prevention (DLP), threat protection, digital experience monitoring, and unified analytics. These functions are valuable when they support consistent decisions and actionable telemetry; their presence alone does not prove that policies are fully integrated.
SASE vs. SSE vs. Zero Trust: what is the difference?
These terms are related but not interchangeable.
- SASE combines networking and cloud-delivered security into a broader access architecture. SD-WAN is typically part of this scope.
- Security Service Edge (SSE) focuses on the cloud-delivered security services, such as SWG, CASB, ZTNA, and FWaaS. It does not itself include the SD-WAN networking layer.
- Zero Trust is a security approach that avoids granting implicit trust solely because a user or device is on a particular network. Access decisions should be based on appropriate verification and policy.
A company can adopt SSE before modernizing its WAN. Another may implement SD-WAN and cloud security together as part of a SASE initiative. Both approaches can be valid, depending on the existing environment and priorities.
Likewise, a SASE deployment can support Zero Trust objectives, but it does not guarantee them. Weak identity controls, excessive permissions, incomplete application coverage, and ungoverned exceptions can undermine the intended security outcome.
What business problems can SASE solve?
1. Inconsistent security between offices and remote users
Different access paths can lead to different policy enforcement. A well-designed SASE architecture can reduce these inconsistencies by applying security services across relevant users, locations, and application types.
2. Unnecessary traffic backhauling
Routing SaaS traffic through a distant data center can add latency and complexity. Distributed inspection may offer a more direct path, provided routing, provider coverage, application behavior, and local network conditions are validated.
3. Excessive operational fragmentation
Multiple products can create separate policy stores, consoles, investigation workflows, and ownership boundaries. Convergence may simplify administration, but only when integrations are mature and operational responsibilities are clearly defined.
4. Overly broad private application access
Replacing selected network-level access patterns with application-specific policies can reduce exposed services and improve segmentation. The security benefit depends on accurate application discovery, identity assurance, device signals, and exception governance.
5. Limited visibility across hybrid environments
Shared logging and analytics can make troubleshooting and security investigations more effective. Organizations should verify whether telemetry is sufficiently complete, exportable, and correlated across all enforcement points.
The risks and trade-offs that deserve attention
SASE should not be positioned as a frictionless migration. Several architectural decisions can materially affect security and user experience.
- Provider dependency: cloud service availability, geographic coverage, and routing decisions can influence access to business-critical applications.
- Inspection limitations: encrypted traffic, privacy requirements, unsupported applications, and certificate management can restrict inspection in some scenarios.
- Legacy application dependencies: applications that assume fixed IP addresses, specific network paths, or unusual protocols may require special treatment.
- Identity and endpoint readiness: inaccurate identity data or unreliable device posture signals can create both security gaps and user disruption.
- Policy migration: reproducing every historical firewall rule or exception without review can preserve unnecessary risk.
- Commercial complexity: licensing, bandwidth assumptions, support ownership, and contract boundaries need a realistic total-cost assessment.
The right question is not whether a vendor supports every acronym. It is whether the chosen architecture meets the organization’s real access patterns, performance requirements, control objectives, and operational constraints.
How to build a practical SASE adoption roadmap
A phased plan helps reduce migration risk while creating evidence of business value.
Days 1–30: establish the baseline
- Inventory users, branches, private applications, SaaS services, and major access methods.
- Identify priority security risks and existing operational pain points.
- Measure current performance, connectivity incidents, VPN dependence, and support volumes.
- Define the ownership model for identity, network, endpoint, security, and application teams.
- Choose a limited pilot population and agree on success criteria.
Days 31–60: pilot, validate, and refine
- Test representative user journeys across office, home, and mobile connectivity.
- Validate access to critical applications, including unusual protocols and third-party dependencies.
- Measure latency, authentication friction, support requests, and policy enforcement.
- Check logging, incident-response workflows, resilience, and fallback procedures.
- Document and govern exceptions rather than silently bypassing new controls.
Days 61–90: expand with evidence
- Extend the rollout to additional populations and applications in risk-based waves.
- Compare security and experience indicators against the original baseline.
- Reduce unnecessary legacy access paths once replacement controls are verified.
- Review unresolved gaps with business and technical stakeholders.
- Set the next adoption milestones and operational review cadence.
This 90-day structure is an illustrative planning framework, not a promise that complex enterprises can complete a full SASE transformation in three months.
Measuring SASE success: beyond deployed users
Deployment statistics matter, but they should be paired with outcome-oriented metrics.
- Application coverage: percentage of critical applications accessed through approved, validated security paths.
- Legacy exposure: reduction in unnecessary network-level remote access and externally reachable services.
- Policy effectiveness: number, age, and risk level of unmanaged exceptions.
- User experience: application response time, failed access attempts, and access-related support tickets.
- Operational performance: time required to investigate and resolve access or policy incidents.
- Resilience: tested recovery procedures and validated behavior during provider or connectivity disruptions.
Segment these measures by application criticality, business unit, geography, and device type. Enterprise-wide averages can conceal difficult experiences or unacceptable exposure in important groups.
The role of Customer Success in a SASE transformation
A SASE migration is rarely just a technology deployment. It crosses teams that do not always share the same priorities: security wants stronger controls, networking wants reliable paths, operations wants manageable workflows, and business units want uninterrupted access.
Customer Success can connect those priorities through a documented success plan, shared milestones, adoption monitoring, and regular stakeholder reviews. Technical validation must be paired with conversations about why the investment was made and what has changed for the organization.
Strong reviews should distinguish activities (policies configured, users provisioned, sites connected) from outcomes (less exposure, fewer avoidable access problems, better visibility, more reliable operations). This difference is crucial when demonstrating value to executive stakeholders.
Questions to ask before selecting a SASE solution
- Which deployment paths and application protocols are fully supported, and which require exceptions?
- How does the provider enforce policies for managed and unmanaged devices?
- What happens when a cloud enforcement point, identity provider, or regional connection becomes unavailable?
- How are logs exported, retained, and correlated with existing security tools?
- What measurable user-experience data is available during and after migration?
- Can the organization retain existing SD-WAN investments while adopting SSE first?
- What responsibilities remain with the customer, the service provider, and any implementation partner?
Frequently asked questions
Is SASE the same as Zero Trust?
No. SASE is an access and networking/security architecture. Zero Trust is a security approach that guides how trust and authorization decisions should be made. SASE capabilities may help implement Zero Trust policies, but architecture and policy design still matter.
Does every company need to deploy SD-WAN and SSE at the same time?
No. Some organizations begin with SSE to secure user-to-internet, SaaS, and private application access, while maintaining their current WAN. Others modernize networking and security together.
Can SASE eliminate every VPN and firewall?
Not necessarily. Some legacy applications, network protocols, site connectivity needs, and regulatory or operational constraints may require complementary controls. The target architecture should be based on validated use cases rather than a blanket replacement claim.
How long does SASE adoption take?
There is no universal timeline. Duration depends on application complexity, organizational size, existing infrastructure, policy maturity, endpoint readiness, and change-management capacity. A pilot can be relatively short; enterprise-wide transformation may take substantially longer.
Final thoughts
SASE offers a useful direction for organizations dealing with distributed users, hybrid applications, and fragmented security controls. But the real measure of success is not how many acronyms appear in the platform specification.
The objective is to provide reliable access, apply appropriate protections, reduce unnecessary exposure, and give teams the visibility and operational maturity required to sustain those results. That requires an architecture grounded in business needs, disciplined rollout, and continuous validation.
When networking, security, and Customer Success work from a shared definition of outcomes, SASE becomes more than a technology project: it becomes an ongoing improvement in how the organization connects and protects its people and applications.
Further reading